AI governance is often discussed as policy: principles, review boards, model cards and risk classifications. Those are useful, but governance becomes real only when it is expressed in product behavior.
A system is governed when it knows what it knows, knows what it does not know, limits what it may do, and leaves evidence of important decisions.
Start with truth-state design
One of the most underestimated AI risks is not hallucination. It is false certainty created by software around the model.
Consider four states:
- a query succeeded and returned zero;
- a query succeeded and returned no rows;
- the system does not have permission;
- the query failed.
These are operationally different. If an application collapses them into the same empty state, an AI agent may infer “nothing exists” when the truth is “we could not measure it.”
For finance, permissions, customer records and operational status, that distinction is essential.
Decision rights should be explicit
Every AI-assisted workflow should define who or what has the right to:
- recommend;
- draft;
- approve;
- execute;
- reverse;
- override.
This should not live only in a policy document. It should be enforced in application permissions, APIs and workflow states.
A human-in-the-loop pattern is useful when actions are consequential, ambiguous or difficult to reverse. But human review should not become a decorative checkbox. The reviewer needs the evidence required to make a meaningful decision.
Evidence is part of the product
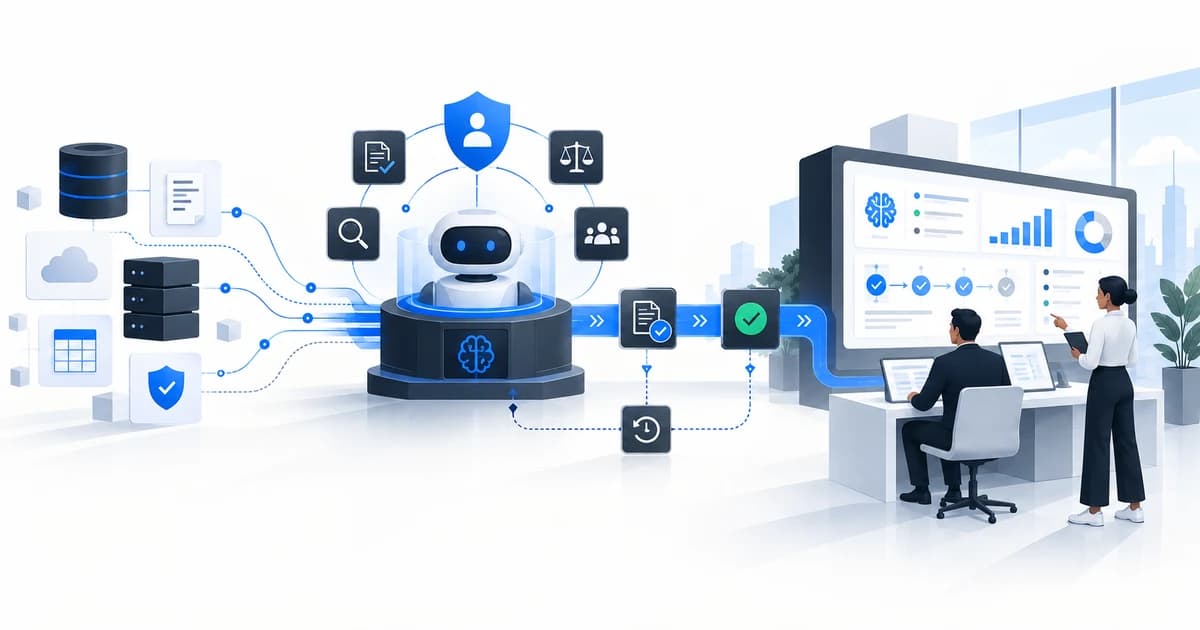
An AI system that changes a business record should preserve enough context to reconstruct the action later.
Depending on risk, that may include:
- user or machine identity;
- input source;
- retrieved evidence;
- recommendation;
- approval state;
- tool/action executed;
- timestamp;
- model/version;
- result and exception path.
This is not only for compliance. It improves debugging, user trust and product learning.
Govern the workflow, not only the model
A model may be statistically strong while the surrounding workflow is unsafe. For example:
- the model recommends the correct customer but the software writes to the wrong tenant;
- the model reads the right invoice but a duplicate webhook creates two payments;
- the model is accurate but uses an overprivileged service credential;
- the model produces a useful answer but the source data was stale.
AI risk therefore belongs to the full lifecycle: data, model, tools, identity, workflow, user interface and monitoring.
NIST's AI Risk Management Framework is helpful precisely because it encourages organizations to govern, map, measure and manage AI risk across the lifecycle rather than reduce governance to one technical control.
Autonomy should expand through evidence
Instead of deciding that a system is either “manual” or “fully autonomous,” organizations can increase autonomy gradually.
A sensible path is:
- AI recommends, human executes.
- AI prepares the action, human approves.
- AI executes low-risk cases, humans review exceptions.
- AI executes within bounded policy and is monitored by outcome metrics.
Autonomy grows when reliability, control and economics have been demonstrated—not because the model is fashionable.
Governance can increase speed
Poor governance slows teams because every AI use case becomes a special exception. Good governance creates reusable patterns: identity, permission, audit, review, evaluation and deployment controls.
That lets product teams move faster because the boundaries are already known.
At NAIT, we view AI governance as an engineering and product-design discipline. The objective is not to eliminate experimentation. It is to make experimentation safe enough that successful ideas can become real operating capability.